Is my Lovable app secure?
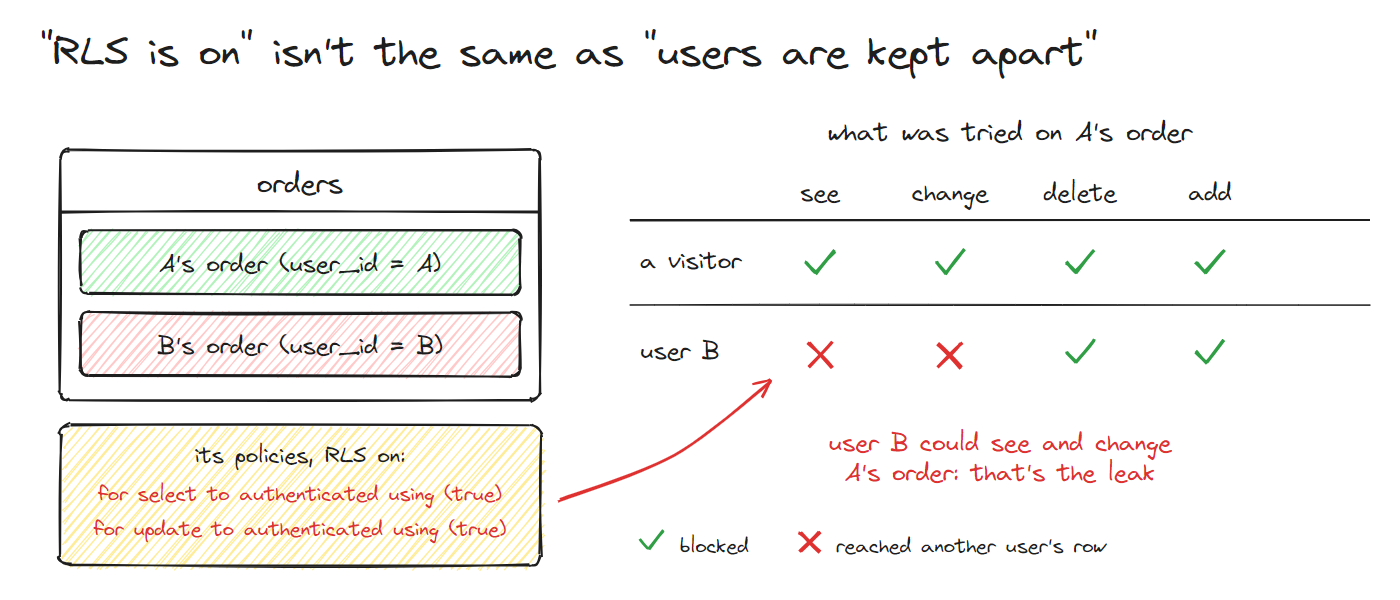
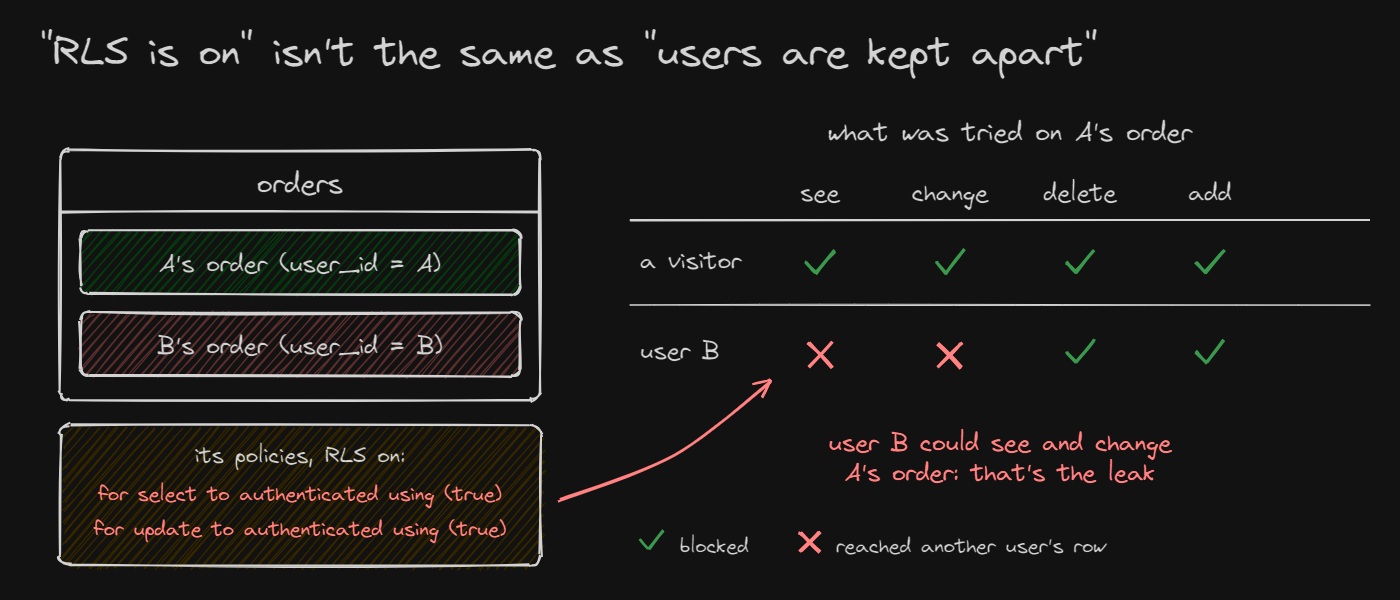
Apps built with Lovable or Bolt talk to Supabase straight from the browser, with a key every visitor gets. That key isn't what keeps your users' data private. The database's row-level security rules are, and when they're missing or too loose, anyone can read, and often change, other people's data.
How common it is
In 2025 a scan of 1,645 Lovable apps found 170 that exposed their users' data this way (CVE-2025-48757). When we ran rls-probe on 25 open-source apps built with Lovable, Bolt or by hand, it flagged 14 of them with at least one critical or high problem.
The holes that come up most
- Database functions anyone can call. A function marked
security definerruns with full rights, skipping every rule. In 15 of the 25 apps, visitors or any signed-in user could call one. In 5, rls-probe called one as a visitor who wasn't signed in, and it deleted or changed another user's data. - Rows created in someone else's name. An insert rule that doesn't check who's inserting lets one user post messages or notifications that look like another user's (10 apps).
- Visitors who can change data. Rules that let anyone, signed in or not, add or edit rows (9 apps).
- File storage open to everyone. Buckets where anyone can upload into, replace or delete other people's files (8 apps).
- Server functions anyone can run. Edge functions with their login check turned off and no check of their own (6 apps).
- The secret key in the browser. The service role key, or an
sb_secret_key, in front-end code skips every rule for whoever copies it. See what to do if yours leaked.
How to check yours
- Get your app's code. In Lovable, connect GitHub and copy the repository link. In Bolt, use Download.
- Paste the link, or drop the ZIP, into rls-probe. It rebuilds your database in your browser, signs in two test users and tries to read and change each other's data. Nothing is uploaded, and your live database is never touched.
- Copy the fix it writes and paste it into Lovable's chat. It names your own tables and rules, so Lovable changes the right thing.
- Check again once Lovable has made the changes.
If your app runs on Lovable Cloud
Lovable Cloud projects are managed by Lovable and don't appear in a Supabase dashboard, so fix them through Lovable's chat. The request rls-probe writes is made for that.
Check your app now
Inspect it in the browser. It takes a few seconds and gives you a grade from A to F.
Sources: CVE-2025-48757; Supabase, Can't access a Lovable Cloud project. The 25-app figures come from running rls-probe 0.5 on public repositories; they're findings to check, not confirmed breaches.