Fixing “permission denied” (42501) after October 30
If a new feature in your Supabase app shows nothing, or an error like permission denied for table orders (code 42501), this is almost certainly why.
What changed
Supabase used to give every new table in the public schema to three roles: visitors (anon), signed-in users (authenticated) and your server (service_role). Row-level security then decided which rows each of them could reach.
Projects created since May 30, 2026 no longer get that. From October 30, 2026, neither does any project, for tables created from then on. Tables you already had keep their access. A table nobody granted answers 42501, to your users and to your edge functions alike.
The quick fix that leaks data
The fix going around is to grant everything, on every table, to everyone. On a table whose row-level security is off, or whose policy says using (true), that grant is exactly what lets anyone read or change every row.
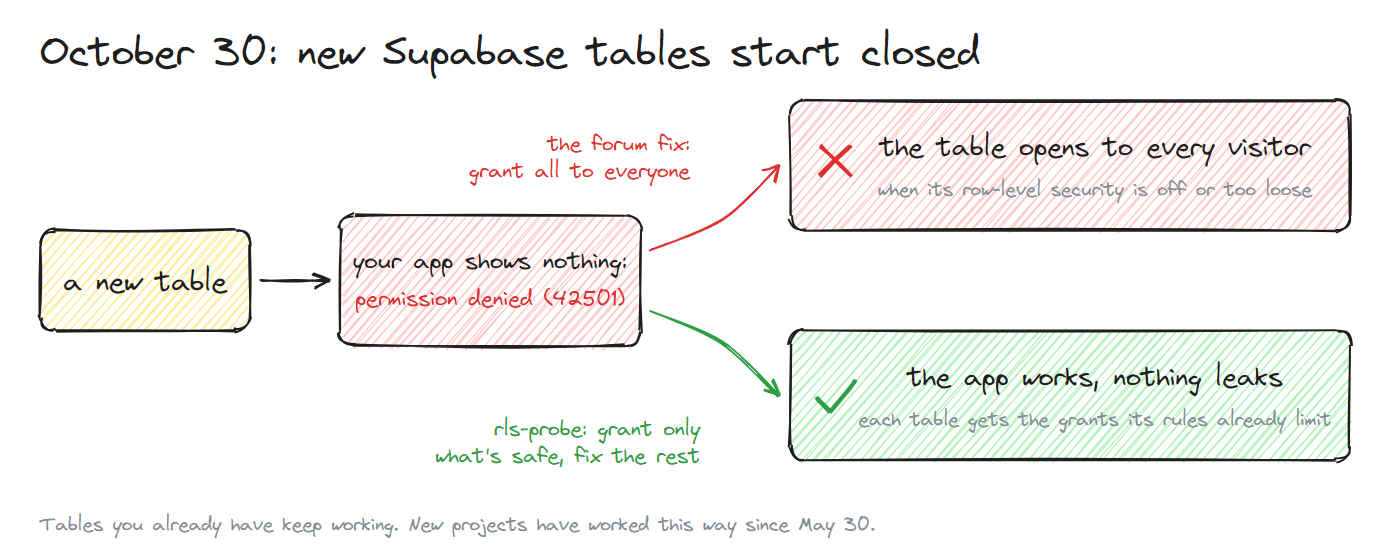
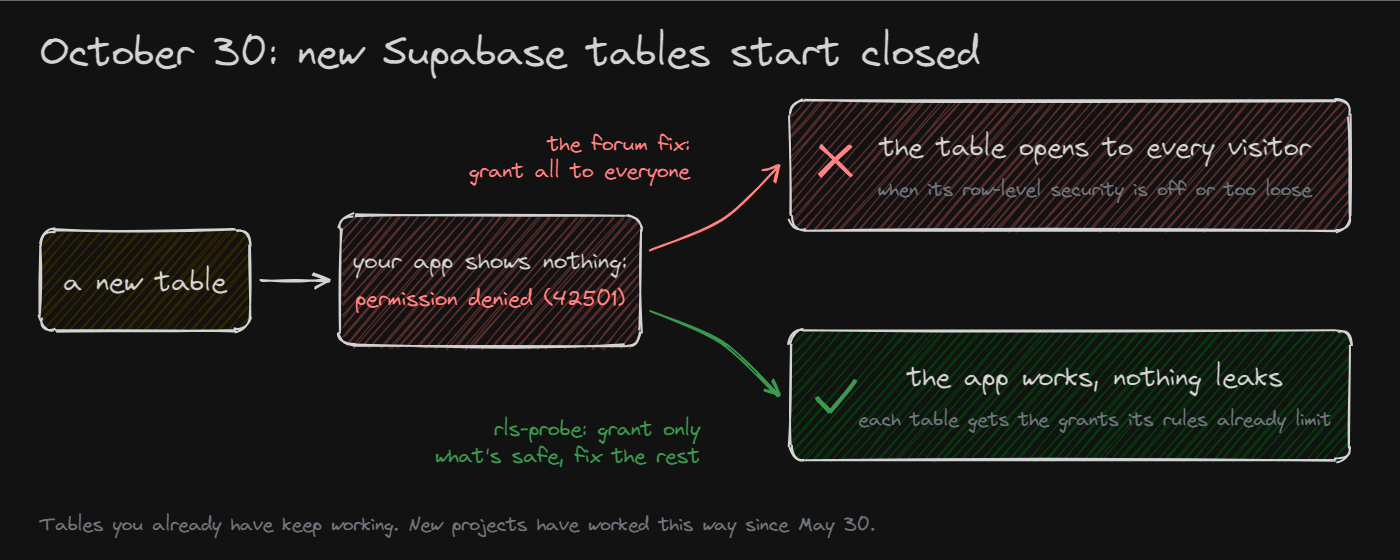
The fix that doesn't
Grant each table only what its policies need, in the same migration that creates it:
create table public.notes (
  id uuid primary key default gen_random_uuid(),
  user_id uuid not null references auth.users,
  body text
);
alter table public.notes enable row level security;
create policy "Owners manage their notes" on public.notes for all to authenticated
  using (user_id = (select auth.uid())) with check (user_id = (select auth.uid()));

grant select, insert, update, delete on public.notes to authenticated;
grant select, insert, update, delete on public.notes to service_role;
- Grant
anononly on tables visitors should read, and usually onlyselect. - Grant
service_roletoo, or edge functions using the secret key get 42501 on the new table. - If users insert rows into a table with a
serialid, grantusageon its sequence as well.
If you build with Lovable or Bolt
Ask for the grants up front. A request that works: “When you create a table, add GRANT statements for anon only if visitors should read it, for authenticated, and for service_role, and enable RLS with policies, in the same migration.”
See which grants are safe for your app
rls-probe rebuilds your database from its migrations and sorts every table: safe to grant (with the exact lines), fix first (a grant would expose data), and closed only because nothing grants it yet. Its suggestions were checked against a real Supabase opted into the change: all 100 checks agreed on a 15-table app built with Lovable.
Inspect your app in the browser, or run npx rls-probe . --fix to write the safe grants as a migration.
Source: Supabase's announcement of the change, github.com/orgs/supabase/discussions/45329.